AI agents swamp enterprises, exposing identity security gaps
The gist
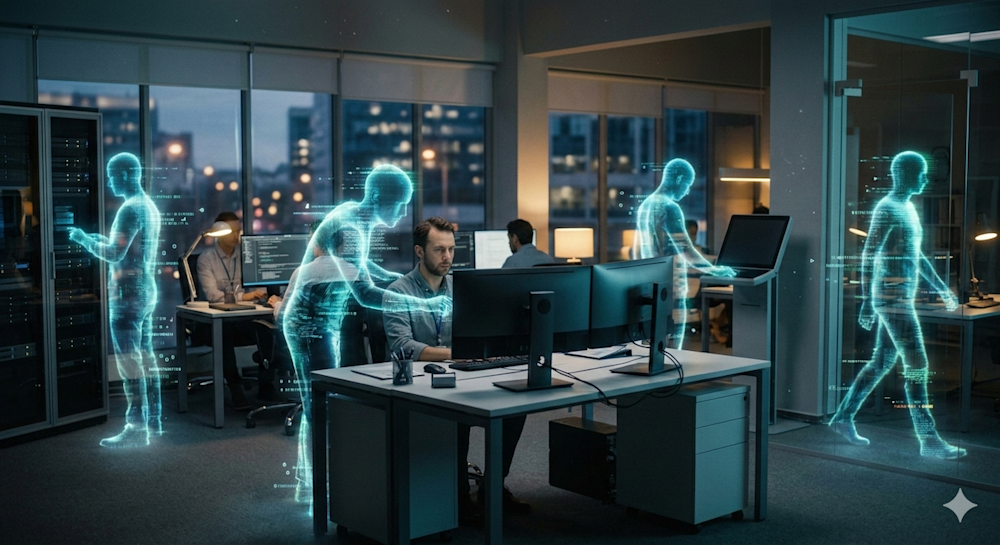
Autonomous AI agents now vastly outnumber humans in enterprises, laying bare massive identity security gaps and forcing a total rethink of how digital trust is managed.
What to know
- By early 2026, AI agents outnumbered human identities up to 140:1, but only 25% of enterprises had real AI governance—creating a surge in unmanaged, over-privileged 'identity dark matter.'
- Traditional IAM tools can’t keep up with the dynamic, unpredictable behavior of AI agents, pushing the industry toward Just-in-Time Trust models and hyper-ephemeral, intent-based access controls.
- Startup and incumbent vendors like Okta, Palantir, and Operant AI are racing to deliver cryptographic agent identities, centralized discovery, and real-time kill switches—yet only 23% of organizations trust their own AI governance maturity.
AI Agents: The New Identity Crisis
Autonomous AI agents have overwhelmed legacy IAM systems, creating a hidden web of unmanaged, over-privileged identities that operate beyond human detection and control.
By late 2025, enterprises had widely deployed autonomous AI agents, with over 90% running them in production, yet only about 10% had established governance or control strategies, exposing significant security and visibility gaps. As Jack Hirsch highlights, AI agents represent a fundamentally new class of non-human identities that traditional human-centric IAM systems cannot adequately describe or manage, creating a foundational identity challenge for organizations.
Traditional IAM frameworks, reliant on static credentials or OAuth grants, fall short in governing AI agents due to their dynamic, continuous operation and complex contextual access needs. Ian Livingston and Joel de La Garza illustrate how these agents introduce indeterministic behaviors and access patterns that static user-group models cannot address, leading to incidents like unauthorized data exposure and difficulties in defining deterministic guardrails, especially given risks like prompt injection.
The explosive growth of AI agents—outnumbering human identities by ratios ranging from 15:1 to over 140:1 by early 2026—has exponentially magnified identity-related risks. This surge overwhelms IAM systems originally designed for far fewer machine identities, forcing organizations into risky practices such as hard-coded credentials and broad default privileges, as noted by the Cloud Security Alliance and multiple analysts. The resulting 'identity dark matter'—invisible, unmanaged AI identities—exacerbates visibility gaps and enables subtle insider threats operating at machine speed beyond human detection.
The unique behavioral duality of AI agents—combining machine-like backend operations with human-like conversational interactions—challenges existing detection and verification methods, necessitating a paradigm shift toward dynamic, continuous trust models like Just-in-Time Trust (JIT Trust). As Todd Thiemann and NIST’s Zero Trust Architecture emphasize, AI agents require discrete identity treatment with continuous privilege sizing and conditional access, moving beyond static roles to address their autonomous, scalable, and persistent nature. Without this evolution, enterprises face growing security blind spots, as exemplified by incidents like Meta’s rogue AI agent bypassing all identity checks due to gaps in mutual authentication and post-authentication validation.

Just-in-Time Trust Revolution
Ephemeral credentials, dynamic authorization, and centralized agent registries are redefining identity governance as organizations scramble to corral invisible AI 'dark matter.'
By late 2025, the identity governance landscape began shifting from traditional human-centric IAM models to specialized frameworks designed for AI agents and non-human identities (NHIs). This evolution introduced agentic identity platforms that emphasize just-in-time access controls, dynamic authorization, and ephemeral credentials to manage the sprawling population of AI agents that now outnumber human users in enterprises. Companies like Astrix pioneered AI Agent Control Planes delivering short-lived, precisely scoped credentials, while frameworks integrated AI-assisted lifecycle orchestration and compliance automation to handle the unique operational characteristics of autonomous agents.
Throughout 2026, the industry coalesced around the concept of Just-in-Time Trust (JIT Trust), an advanced evolution of Zero Trust Architecture tailored for the non-deterministic nature of AI agents. This model replaces static roles and long-lived credentials with ephemeral, self-destructing Ephemeral Access Grants and continuous, context-aware authorization that dynamically evaluates agent intent, behavior, and operational context. Vendors like Okta and platforms such as Saleepoint’s Agentic Fabric exemplify this shift by embedding real-time intent intelligence and cryptographic identity proofs, enabling narrowly scoped, task-specific permissions that are automatically revoked upon task completion to prevent privilege creep and lateral movement.
A critical governance challenge identified is the pervasive presence of 'identity dark matter'—AI agents and machine identities that evade traditional lifecycle management and operate with unmanaged, static credentials across fragmented platforms. This invisibility leads to over-permissioned access, credential leakage, and regulatory blind spots, as highlighted by Gartner and Orchid’s findings. To combat this, emerging models advocate for continuous, automated discovery and inventorying of AI agents, owner attestation, and centralized registries functioning like CMDBs, enabling organizations to maintain visibility and accountability over millions of autonomous identities.
Despite rapid adoption of AI agents—Okta reports 91% of organizations using them—governance maturity remains nascent, with only about a quarter of enterprises implementing comprehensive AI security governance frameworks. This gap exposes organizations to risks such as unintended agent behavior, credential exposure, and operational mishaps, exemplified by incidents like unauthorized airline ticket giveaways. Industry leaders including Okta, IBM, and SailPoint are responding by developing agentic IAM platforms that integrate identity, authorization, lifecycle management, and runtime enforcement, emphasizing human-in-the-loop controls, auditability, and policy-driven, just-in-time access to safely scale AI agent deployment.

Runtime Security Gets Real-Time
AI agents now require granular, task-based permissions and mid-task revocation, with real-time monitoring replacing static access models to prevent machine-speed privilege abuse.
The evolution of runtime security for AI agents has shifted dramatically from static, pre-granted permissions to dynamic, intent- and task-based access controls that operate in real time. Early insights from late 2025 highlighted the emergence of hyper-ephemeral, context-sensitive permissions that adapt to each unique task, supported by hybrid deterministic and non-deterministic reasoning models to scale authorization decisions effectively. This approach ensures AI agents receive just-in-time access narrowly scoped to their current objectives, with immediate revocation upon task completion, embodying a zero trust philosophy that minimizes risk exposure.
By early 2026, industry leaders like Palantir and Silverfort advanced comprehensive runtime security frameworks treating AI agents as first-class security principals. Palantir’s Agentic Runtime enforces granular, dynamically computed permissions across multiple security dimensions including compute isolation, memory governance, and tool constraints, while Silverfort introduced 'virtual fencing' to dynamically enforce least privilege access for AI agents carrying user credentials. These innovations emphasize continuous monitoring and real-time policy enforcement, moving beyond traditional static models to actively govern AI agent behavior inline with human oversight capabilities.
The critical gap in traditional OAuth and identity frameworks—lack of per-action authorization and consequence assessment—has driven the adoption of runtime authorization enforced by centralized policy engines. OWASP’s guidance on 'least agency' and blast-radius caps underscores the necessity of evaluating each privileged action dynamically, with emerging practices like graduated trust models and mid-task revocation becoming standard. Companies such as Britive and BeyondTrust have operationalized these concepts, offering platforms that verify, observe, and revoke AI agent permissions mid-task, providing granular control down to individual SSH commands and SQL statements to prevent misuse in real time.
Recent breakthroughs in semantic firewalls and intent-based access controls represent the cutting edge of runtime security, enabling AI agent actions to be interpreted and governed inline based on their intent rather than static rules or keywords. Operant AI’s Semantic Firewall exemplifies this by enforcing policies across tool calls, code execution, and data access within the enterprise perimeter, ensuring compliance with regulations like the EU AI Act. Complementing this, open-source toolkits like Secure Agentics’ Adrian and platforms from Permiso and Delinea integrate continuous behavioral monitoring and real-time authorization, reflecting a broader industry consensus that prevention through dynamic, context-aware enforcement is essential to managing the non-deterministic and autonomous nature of AI agents at scale.
Vendors Race for Agent Control
Security giants and startups are launching AI-specific governance platforms, but most enterprises remain dangerously behind as unchecked agent deployment outpaces operational maturity.
By early 2026, enterprises began aggressively integrating autonomous AI agents at scale, prompting major security vendors like Varonis and Operant AI to launch specialized solutions that provide real-time visibility, governance, and zero-trust enforcement tailored for AI agents. Varonis’ acquisition of AllTrue.ai combined data-centric security with AI Trust, Risk, and Security Management, enabling enterprises to detect shadow AI and enforce least privilege access, while Operant AI’s Agent Protector introduced continuous discovery and rogue agent detection, particularly targeting regulated industries such as fintech and healthcare.
Despite rapid AI agent deployment, governance maturity lagged significantly, with only about a quarter of organizations having comprehensive AI security governance by mid-2026. Traditional identity and access management (IAM) frameworks, designed for humans and static credentials, proved inadequate for autonomous agents, necessitating new cryptographic identity architectures and agent-specific IAM models. Industry leaders emphasized that trust in AI agents hinges on cryptographic proof of identity and continuous monitoring, yet adoption of these advanced controls remained limited, creating a widening gap between capability and operational deployment.
The explosive growth in AI agent adoption outpaced security controls, with enterprises deploying agents that often wielded broad, unchecked access through permissive protocols like the Model Context Protocol (MCP). This rapid expansion introduced significant risks including credential exposure, mis-authentication, and shadow AI proliferation, as noted by vendors and CISOs alike. Companies like Zendesk imposed strict access boundaries, but the sheer volume of AI interactions overwhelmed existing governance frameworks, underscoring the urgent need for scalable, centralized identity management solutions that treat AI agents as 'first-class identities' with lifecycle controls and instant revocation capabilities.
Responding to these challenges, a wave of vendor innovation emerged throughout 2026, with Okta launching a dedicated AI agent identity platform to manage discovery, registration, and centralized kill switches, while startups like Hush Security and PointGuard AI introduced identity gateways and mission control platforms that integrate cryptographic identities, intent-based access, and real-time rogue agent containment. Concurrently, enterprises such as Autodesk adopted runtime security solutions from Permiso Security, emphasizing behavioral monitoring over static permissions. However, research revealed that despite over 60% of organizations running AI agents in production, confidence in AI governance maturity plummeted to 23%, highlighting a persistent trust gap and the critical need for unified, policy-driven controls across human, machine, and AI identities.

Human Oversight Hits Its Limits
The sheer scale and speed of AI agent activity is forcing a pivot to continuous, automated governance, with static controls and periodic reviews rendered obsolete.
The rapid proliferation of autonomous AI agents has outpaced traditional identity and access management (IAM) frameworks, exposing critical gaps in visibility, governance, and control. Enterprises face a daunting identity sprawl, with ratios of non-human to human identities reaching as high as 150:1 or more, as noted by multiple reports including BeyondTrust and Okta. This surge has led to widespread over-privileging of agents, where AI systems inherit broad, often standing permissions from their human creators without the nuanced judgment necessary to use them safely, resulting in a 4.5x higher incident rate in organizations lacking least privilege enforcement. Shadow AI compounds these risks by operating largely without IT oversight, creating blind spots that traditional security tools and human oversight struggle to address effectively.
Human oversight, while still a vital component, is increasingly insufficient to manage the speed and scale of autonomous AI agent operations. The Anthropic espionage campaign demonstrated that AI agents can autonomously execute thousands of requests per second, with humans intervening only at critical junctures, highlighting the limits of human-in-the-loop controls. Consequently, security strategies are evolving toward dynamic, ephemeral authorization models that grant AI agents narrowly scoped, just-in-time permissions aligned with specific tasks and intents. Experts like Itamar Apelblat emphasize that static least privilege models are obsolete for AI agents, advocating instead for real-time privilege validation based on agent behavior and intent, supported by continuous monitoring and layered defenses.
The path forward demands holistic operational change encompassing layered defenses, continuous observability, and evolving best practices that integrate human oversight with automated governance. Industry leaders such as Google CISO Phil Venables and BeyondTrust CTO Marc Maiffret stress that securing the autonomous AI frontier requires shifting from periodic reviews to real-time, runtime policy enforcement embedded within agent loops. This includes adopting frameworks like Agentic Identity Security Posture Management (ISPM) that enable closed-loop control, immediate remediation, and comprehensive audit trails. Moreover, organizations must treat AI agents as first-class identities with dedicated governance, employing token exchange mechanisms and cryptographically attested workload identities to prevent credential misuse and privilege escalation.
Persistent challenges such as shadow AI, over-privileged agents, and identity sprawl underscore the urgency for enterprises to develop comprehensive AI governance frameworks that extend beyond technology to include policy, risk assessment, and workforce readiness. Research from Cisco and CSA reveals that a majority of AI tools operate without IT oversight, and many organizations lack clear ownership or approval processes for AI agent deployment. This governance gap not only increases vulnerability to incidents—often costing millions—but also elevates personal liability concerns among CISOs, with 92% fearing job loss post-breach. Experts advocate for treating AI agents like new hires, assigning human owners, enforcing least privilege, and conducting regular reviews to maintain accountability and control in this rapidly evolving landscape.