Quantum-safe hardware race heats up as SEALSQ, MIT, and global partners forge next-gen security ecosystem
The gist
The global race to build quantum-safe hardware is exploding, with SEALSQ, MIT, and a growing roster of heavyweight partners rolling out next-gen silicon to outpace looming quantum threats.
What to know
- SEALSQ's QS7001 microcontroller, packing NIST-approved Dilithium 5 and Kyber algorithms, promises up to 10x performance gains and robust tamper resistance by early 2026 across sectors like robotics and infrastructure.
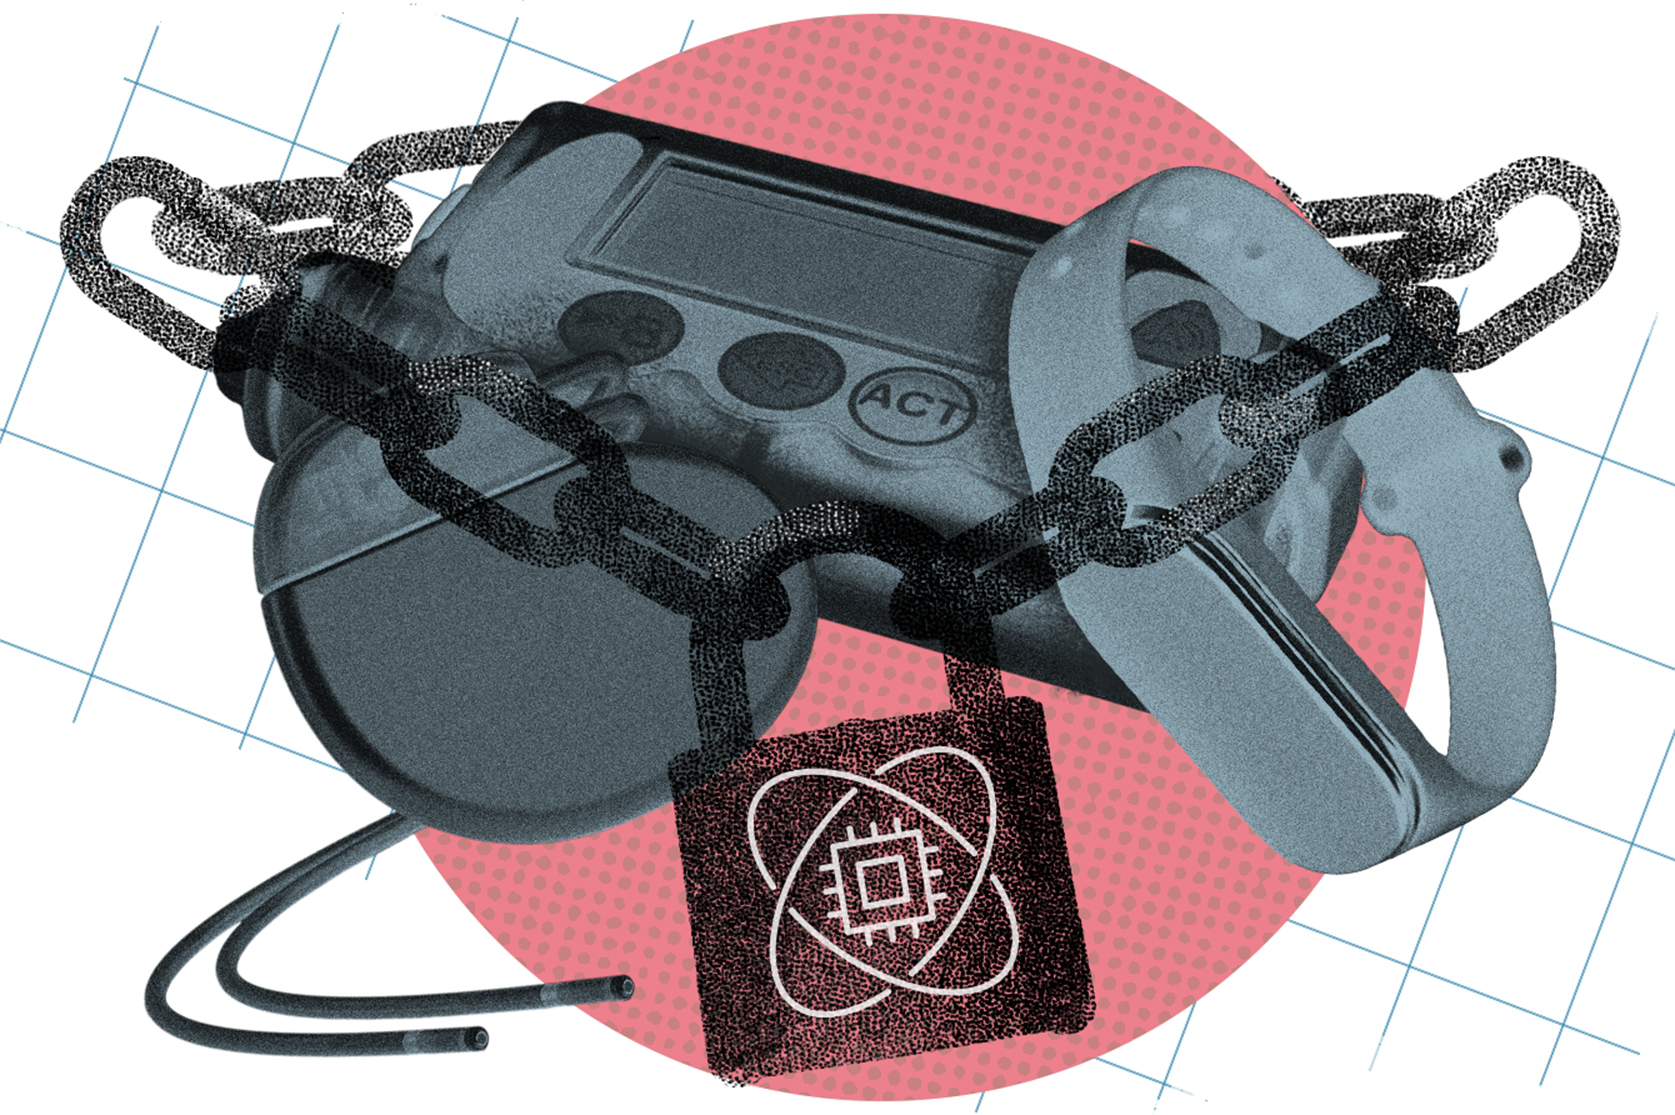
- MIT’s needle-tip-sized chip delivers 20-60x better energy efficiency for pacemakers and biomedical devices, defending against both quantum and physical attacks.
- Quantum eMotion, JMEM TEK, and allies are targeting a 2027 launch for a Universal Security SoC with PQC accelerators, quantum entropy, and hardware roots of trust, aiming to protect AI data centers, defense, and autonomous vehicles.
Silicon-Deep Security Shift
SEALSQ, MIT, and global partners are embedding quantum-safe cryptography directly into hardware, setting new standards for tamper resistance, regulatory compliance, and sector-wide trust from robotics to biomedical implants.
By early 2026, SEALSQ had firmly established itself as a pioneer in silicon-based post-quantum cryptography hardware with its QS7001 microcontroller, which integrates NIST-approved algorithms like ML-DSA-87 (Dilithium 5) and ML-KEM (Kyber) directly into silicon. This integration not only delivers up to 10x performance improvements over software-only implementations but also enhances tamper resistance and side-channel attack protection, positioning the QS7001 as a robust hardware root of trust compliant with emerging legal standards such as CNSA 2.0. SEALSQ’s extensive patent portfolio and over 1.75 billion deployed secure semiconductors underscore its commitment to enabling a certifiable PQC transition across critical sectors including robotics, automotive, and infrastructure.
In parallel, MIT’s breakthrough development of a needle-tip-sized microchip represents a quantum leap in securing power-constrained biomedical devices like pacemakers and insulin pumps. This ultra-efficient chip implements dual PQC schemes alongside an on-chip true random number generator, achieving 20 to 60 times higher energy efficiency compared to prior solutions. By addressing both algorithmic and physical attack vectors—including power side-channel defenses and early fault detection—MIT’s innovation not only extends the operational lifespan of battery-powered implants but also sets a precedent for securing other resource-limited edge devices such as industrial sensors and smart inventory tags.
Looking ahead to 2027, the collaboration between Quantum eMotion and JMEM TEK is advancing the frontier of post-quantum cryptographic hardware through the development of a quantum-resilient Universal Security SoC. This platform integrates PQC accelerators, Physical Unclonable Functions (PUFs), and hardware roots of trust to deliver tamper-resistant, energy-efficient security tailored for high-assurance sectors including AI data centers, defense, and autonomous vehicles. Complemented by FIPS 140-3 and FedRAMP-aligned deliverables such as PCIe boards and Cryptography-as-a-Service appliances, this initiative exemplifies the drive toward certified, sovereign semiconductor supply chains that meet the stringent demands of emerging technology applications.

Compliance Drives PQC Hardware
Regulatory milestones like CNSA 2.0 and FIPS 140-3 are accelerating the move from software to certified hardware roots of trust, with SEALSQ’s QS7001 setting the pace for legally mandated quantum-safe infrastructure.
By early 2026, SEALSQ’s Quantum Shield QS7001 emerged as a pioneering hardware root of trust explicitly designed to comply with stringent new cryptographic legal mandates such as CNSA 2.0. Embedding advanced post-quantum cryptographic primitives like ML-DSA-87 (Dilithium 5) for firmware signing and ML-KEM (Kyber) for key establishment directly into silicon, the QS7001 not only delivers up to 10x performance improvements over software-only solutions but also robust tamper resistance and hybrid cryptographic support. This integration enables secure boot, firmware authenticity, and quantum-safe communication across critical sectors including robotics, automotive, and industrial infrastructure, illustrating how regulatory frameworks are driving a hardware-centric approach to PQC adoption.
Achieving the NIST SP 800-90B Entropy Source Validation Certificate #E333 marked a pivotal regulatory milestone for SEALSQ’s QS7001, underpinning its path toward full FIPS 140-3 compliance—a non-negotiable standard for cryptographic hardware in regulated markets. This certification validates the quality of the QS7001’s ring oscillator-based physical noise entropy source, a foundational element ensuring the module’s cryptographic strength and reliability. Beyond compliance, this milestone strategically positions SEALSQ to integrate validated entropy sources into future products and to license this technology to partners aiming to meet escalating quantum-resistant security demands across industries.
AI Robotics and PQC Converge
WISeKey and SEALSQ’s WISeRobot.ch initiative fuses digital identity, PQC hardware, and human-centric AI to secure machine-to-machine interactions in critical robotics, showcased live at the 2026 World Economic Forum.
By early 2026, SEALSQ had established itself as a pioneer in embedding post-quantum cryptography directly into semiconductor hardware, notably with its Quantum Shield QS7001 microcontroller. This device integrates advanced PQC algorithms like Dilithium 5 and Kyber, delivering up to tenfold performance improvements and robust side-channel attack resistance, positioning SEALSQ to meet stringent new legal standards such as CNSA 2.0. Their strategy of combining hardware roots of trust with PKI solutions aims to future-proof security across diverse sectors including robotics and critical infrastructure, underscoring a holistic approach to quantum resilience.
In the healthcare domain, MIT’s development of a needle-tip-sized microchip tailored for power-constrained biomedical devices like pacemakers and insulin pumps marks a critical leap in PQC application. By implementing dual PQC schemes and sharing computational resources, this chip reduces energy overhead by over an order of magnitude compared to earlier solutions, while incorporating defenses against power side-channel attacks and voltage glitches. Lead researcher Seoyoon Jang highlighted the urgency of securing vulnerable biomedical devices as quantum computing advances and regulatory bodies such as NIST push toward PQC standards, with potential adaptability extending to industrial sensors and smart inventory tags.
The collaboration between WISeKey and SEALSQ to launch WISeRobot.ch exemplifies sector-specific PQC integration in critical infrastructure robotics, blending WISeKey’s digital identity expertise with SEALSQ’s post-quantum semiconductors and PKI infrastructure. This platform, supported by 126 scientific advisors, emphasizes human-centric AI robotics secured at multiple system levels to ensure trusted machine-to-machine interactions, as demonstrated in a live proof of concept at the 2026 World Economic Forum. Carlos Moreira, SEALSQ’s CEO, stressed the imperative of embedding trust and security into intelligent machines from inception, reflecting the growing role of AI and robotics in essential services.
Telecommunications face acute challenges in adopting PQC due to the 3 to 10 times larger key sizes required by new algorithms, which strain resource-constrained IoT devices and risk service disruptions. Analysts recommend a phased rollout starting with comprehensive cryptographic asset mapping and prioritization based on data sensitivity and device lifecycle, while proactively shipping quantum-ready SIMs and eSIMs as a cost-effective foundational step. Industry leaders like Thales, co-author of the Falcon FN-DSA digital signature algorithm with NIST, exemplify active engagement in standardizing PQC to counteract 'Harvest Now, Decrypt Later' attacks targeting subscriber data with long lifecycles.
In the financial sector, SEALSQ’s majority acquisition of Wecan and CHF 5 million investment through its Quantum Fund accelerates the creation of a post-quantum AI-powered compliance copilot tailored for global banks. This initiative integrates quantum-resistant hardware security modules, secure digital identity frameworks like WISeKey’s WISeID, and blockchain-based trust mechanisms to build an end-to-end quantum-resilient platform for banking and digital assets. CEO Carlos Moreira framed this convergence of cybersecurity, compliance automation, digital identity, and trusted AI as a pivotal advancement addressing the quantum era’s unique challenges in finance.
Addressing the Internet of Medical Things (IoMT), researchers proposed a Kubernetes-based federated learning security framework that integrates post-quantum cryptography to reduce latency by 35%, enabling near real-time secure data aggregation. Utilizing lightweight K3s containers and RabbitMQ message queues, the system efficiently manages distributed cryptographic processing on resource-constrained devices, validated on a Raspberry Pi cluster. Security is maintained through ML-KEM0 key encapsulation and Ascon authenticated encryption, balancing strong quantum-resistant protection with minimal processing impact, while the distributed design eliminates single points of failure and supports global model updates in under 1.5 seconds.
IoT Faces Quantum Challenge
Resource-strapped IoT and medical devices are racing to adopt scalable PQC strategies, leveraging hybrid cryptography, federated learning, and quantum-ready SIMs to counteract looming ‘Harvest Now, Decrypt Later’ threats.
By early 2026, SEALSQ pioneered embedding post-quantum cryptography (PQC) algorithms directly into silicon through its QS7001 'Quantum Shield' microcontroller, which integrates NIST-approved standards like ML-KEM/Kyber and ML-DSA/Dilithium. This hybrid cryptographic approach marries mathematical robustness with physical tamper-resistant hardware, creating immutable roots of trust that significantly bolster defenses against AI-driven cyber threats and side-channel attacks. With over 1.75 billion secure semiconductors deployed and a portfolio of 126 active patents, SEALSQ positions itself as a critical enabler for OEMs and infrastructure providers navigating resource constraints while meeting Google’s 2029 PQC migration deadline.
The transition to PQC presents formidable challenges for resource-constrained IoT devices, as new algorithms demand key sizes three to ten times larger than current encryption, straining processing capabilities in telecommunications networks. This expansion exacerbates risks from 'Harvest Now, Decrypt Later' attacks, where adversaries collect encrypted data now to decrypt once quantum computers mature, underscoring the urgency for telcos to adopt phased rollout strategies that prioritize asset mapping and risk assessment. Cost-effective measures, such as provisioning quantum-ready SIM and eSIM cards at no incremental cost, are emerging as pragmatic steps to build a quantum-safe device ecosystem ahead of the 2033 quantum threat horizon.
Innovative frameworks like the Kubernetes-based federated learning system proposed by Alshoghri et al. demonstrate how distributed cryptographic processing can overcome the latency and scalability bottlenecks inherent in resource-limited Internet of Medical Things (IoMT) environments. By leveraging lightweight Kubernetes (K3s) containers and RabbitMQ message queues, this architecture reduces latency by 35% and enhances resilience against single points of failure. Crucially, it employs a balanced cryptographic suite combining ML-KEM0, a post-quantum key encapsulation mechanism, with the lightweight authenticated encryption algorithm Ascon, ensuring robust quantum-resistant security without overwhelming device computational resources.
Industry collaboration is accelerating the standardization of PQC algorithms essential for secure, scalable deployment. Thales’ co-authorship of the ‘Falcon’ FN-DSA FIPS 206 digital signature algorithm alongside NIST exemplifies this cooperative momentum, providing a vetted quantum-safe signature standard that supports the broader transition to post-quantum security. Such partnerships are vital to harmonize cryptographic innovation with practical implementation timelines, helping industries mitigate emerging quantum threats while addressing the resource constraints endemic to modern connected devices.
Global Alliances Forge Trust Chains
Cross-border partnerships—like Quantum eMotion and JMEM TEK’s Universal Security SoC and SEALSQ’s investment in Wecan—are building sovereign, quantum-resilient ecosystems for AI, finance, and critical infrastructure.
The collaboration between Quantum eMotion and JMEM TEK marks a pivotal step in advancing post-quantum security hardware through a Canada–Taiwan consortium focused on developing a quantum-resilient Universal Security SoC, slated for a 2027 launch. This partnership integrates Quantum eMotion’s proprietary quantum entropy source with JMEM TEK’s secure chip design elements such as Physical Unclonable Functions and PQC accelerators, delivering a comprehensive ecosystem approach that meets stringent regulatory standards like FIPS 140-3 and FedRAMP. By targeting critical sectors including AI data centers, defense, autonomous vehicles, and critical infrastructure, the consortium not only addresses quantum threats but also fosters sovereign semiconductor supply chains through co-owned intellectual property and shared commercialization models.
WISeKey and SEALSQ’s launch of the WISeRobot.ch platform exemplifies ecosystem development by embedding post-quantum AI security across critical infrastructure robotics at silicon, firmware, and system levels. Supported by a robust network of 126 scientific advisors, WISeRobot.ch serves as a collaborative hub for advancing deployment use cases and partnerships, with CEO Carlos Moreira emphasizing the imperative of integrating trust, security, and human-centric values into intelligent machines from inception as AI and robotics become integral to vital sectors like government and healthcare.
SEALSQ’s strategic acquisition of a majority stake in Wecan, backed by a CHF 5 million investment from its Quantum Fund, underscores a concerted effort to develop post-quantum AI-powered compliance solutions tailored for financial institutions. This initiative integrates advanced post-quantum cryptography, quantum-resistant hardware security modules, secure digital identity frameworks, and blockchain trust mechanisms, notably collaborating with WISeKey to embed the WISeID digital identity ecosystem. As SEALSQ CEO Carlos Moreira articulates, this convergence of cybersecurity, compliance automation, digital identity, and trusted AI is critical for building end-to-end quantum-resilient trust platforms in the financial sector.